
TPMs are fairly ubiquitous, as they’re current in lots of telephones, routers, servers, laptops and even cloud computing choices. A given TPM may be tied again to its manufacturer via a certificate chain, proving it is an authentic system (as lengthy as the producer protects their non-public certificates), while also containing an encryption key that’s distinctive to this specific TPM. This certificates chain and the cryptographic features allow it for use to boost the safety of a given system with issues corresponding to disk encryption, measured boot and file integrity measurements.
Psa Licensed: Safety Without The Complexity
These malware networks introduce unauthorized code, steal knowledge, or exploit their hosts by way of another means. As A End Result Of gadget producers wish to safeguard their reputations, their IoT gadgets should be safe. With more laws, rules, and standards being created on this vein, safety can’t be imposed as an afterthought.
Selecting An Adequately Safe Rot
Whereas exact definitions can vary considerably, a RoT may be described as a set of implicitly trusted functions that the rest of the system or gadget can use to ensure safety; it’s the basis on which a tool maker can build their “tower of trust”. As organizations move to enhance their zero belief safety posture, hopefully they understand that there ought to be nothing that is trusted implicitly in phrases of interactions with their methods. Wherever attainable, they should search for the option to confirm claims themselves, even when the claims appear to return from a trusted vendor or part.
Why Is A Root Of Trust Necessary For Iot Security?
In a secure system, the RoT performs comparable capabilities, provisioning and storing the cryptographic root key. This secret is the basis for all secure operations, similar to native on-device asset protection for identification, authentication, and secure communication with the exterior environment. As such, the RoT should all the time be trusted by the system and is greatest applied as a Hardware Root of Trust (HRoT) for optimum safety. EnsoLab’s Hardware Root of Belief anchors device identity, secure boot and cryptographic key protection https://crestpointsolution.com/ in hardware, establishing a trusted foundation for the safety layers above. The PSA Root of Belief (PSA-RoT) was developed particularly for IoT and designed to help builders looking to cost-effectively implement IoT security, even on low cost microcontrollers. It offers an easy-to-use safety element implemented by a lot of the world’s main chip distributors.

TypingDNA Confirm 2FA uses Root of Belief on this authentication context for its Normal integration. Before typing biometrics are used for verification, the organization verifies the user’s cellphone quantity or email address because the Root of Belief. If typing verification fails or further verification is required, Confirm 2FA can fall again to an OTP sent by way of that trusted channel.
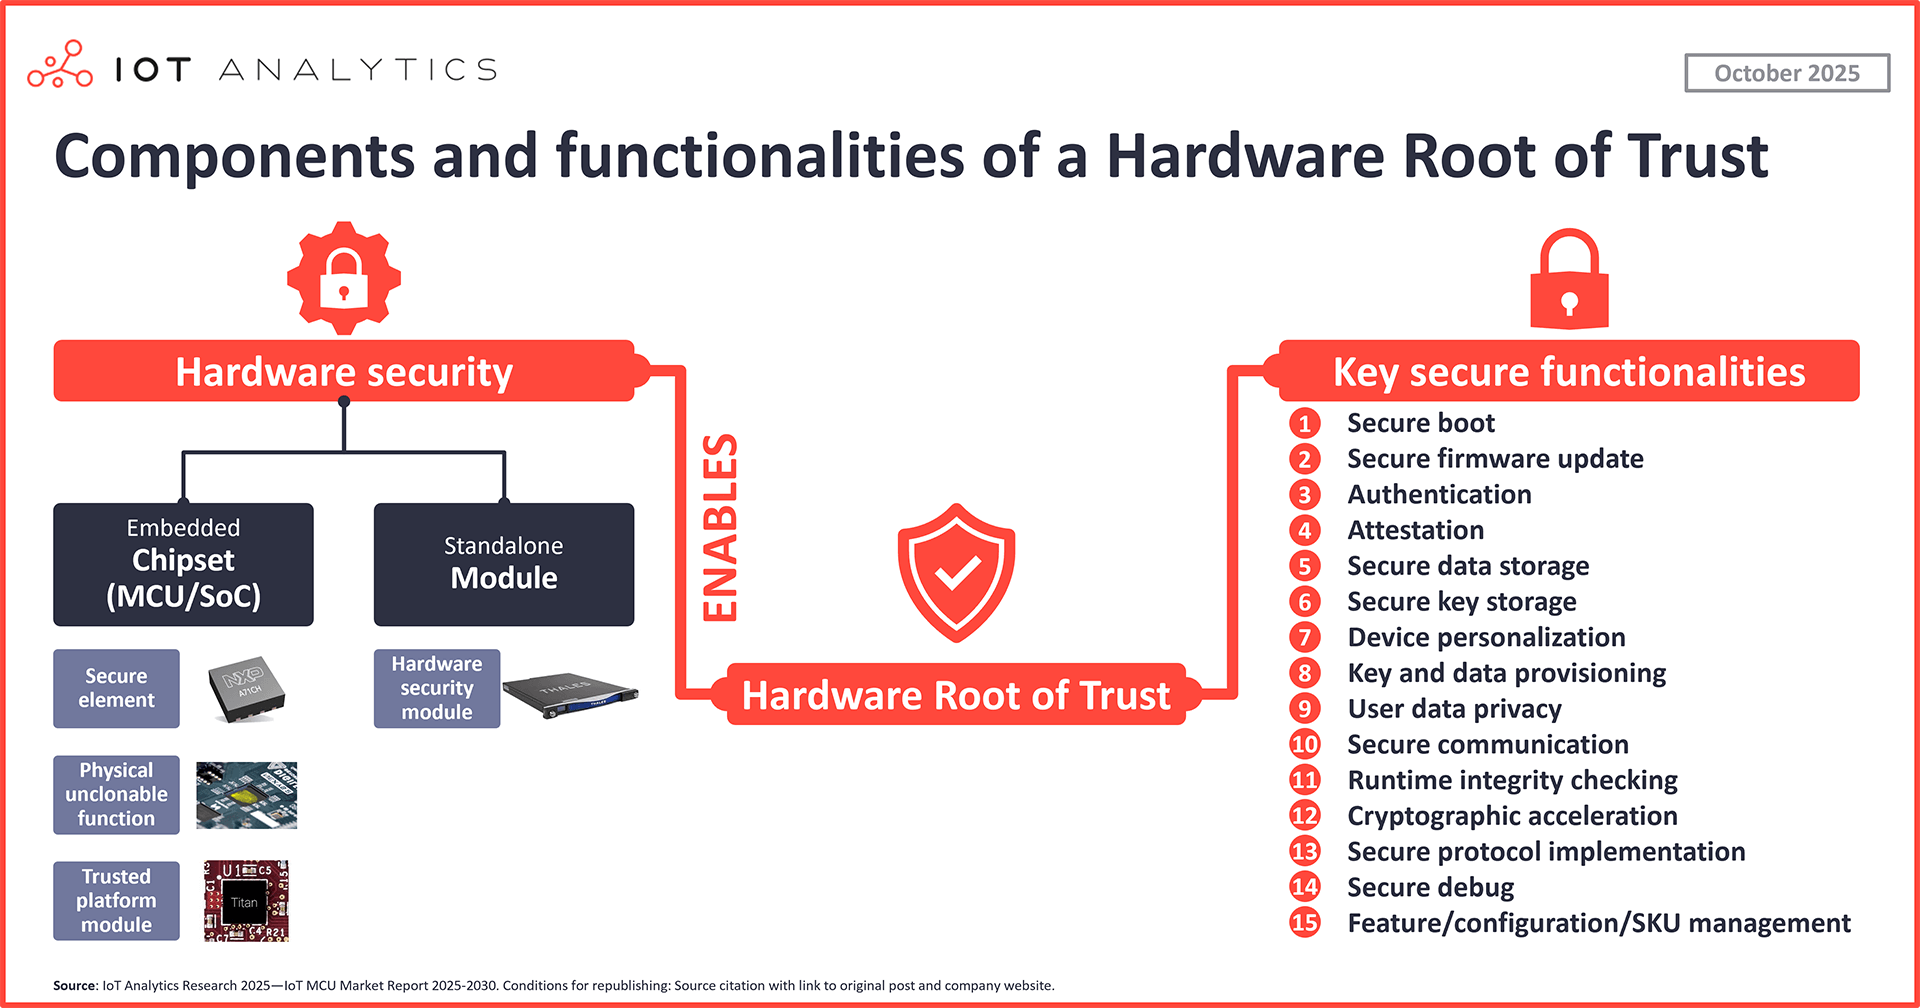
Hardware root of trust may help with a variety of security points which might be primarily divided into pre-boot and post-boot. Pre-boot can use a computer chip referred to as a Trusted Platform Module (TPM) to verify/measure integrity and secure the boot course of from low-level malware. TPM assists with numerous activities throughout post-boot, including root of belief for authentication. Methods that deploy hardware root of belief will use unified extensible firmware interface (UEFI), which provides choices similar to “Secure Boot” that assist prevent attacks or infection from malware.
- TPM assists with varied actions during post-boot, together with root of trust for authentication.
- Securing IoT units is important to protect the system makers popularity with customers and businesses.
- Sourcing the distinctive identifier (UID) and Hardware Distinctive Key (HUK) is a critical utilization of an HRoT.
- Measured Boot creates a detailed log of each element that loaded, permitting a remote verifier to assess the exact configuration of the device.
- With belief comes vulnerability–an particularly uncomfortable idea for those of us primarily involved with security.
His expertise in both startups and huge tech corporations has given him a passion for shifting safety to the left and making it easier to understand and use. The implementations differ in ways in which matter the moment you might be deciding what to trust.
Earlier Than the device software and other system software program start to run, the system must boot and set up the software program running is authentic and has not been tampered with. This course of is called trusted boot and is likely one of the essential functions of a well-designed RoT. Purple Hat is an open hybrid cloud expertise chief, delivering a constant, comprehensive basis for transformative IT and synthetic intelligence (AI) functions within the enterprise. As a trusted adviser to the Fortune 500, Purple Hat provides cloud, developer, Linux, automation, and utility platform applied sciences, as nicely as award-winning services. Lily is a senior software engineer in Pink Hat’s Rising Technologies Safety staff. She has primarily worked on tasks related to remote attestation and confidential computing, and more just lately on securing the software program provide chain.
Comments